Microsoft released this months bulletin a tad bit late. Nontheless, here it is! I half expected a crazy announcement – but fortunately other than crossing the total number of CVEs mitigated compared to the whole of 2025 – this release is nothing exceptional. This month, Microsoft patched 1,413 CVEs this month, plus one republished Cisco Talos CVE. Microsoft Windows alone attributes 1,102. One is exploited in the wild: CVE-2026-96951, a Windows Shell Mark of the Web bypass. One is publicly disclosed: CVE-2026-108398, a .NET Framework bypass of Windows Defender Application Control. Read on for more details.
Read more: Microsoft Patch Tuesday October 2026 Exploitability and Patching PriorityMicrosoft Patch Tuesday October 2026: Numbers/Highlights
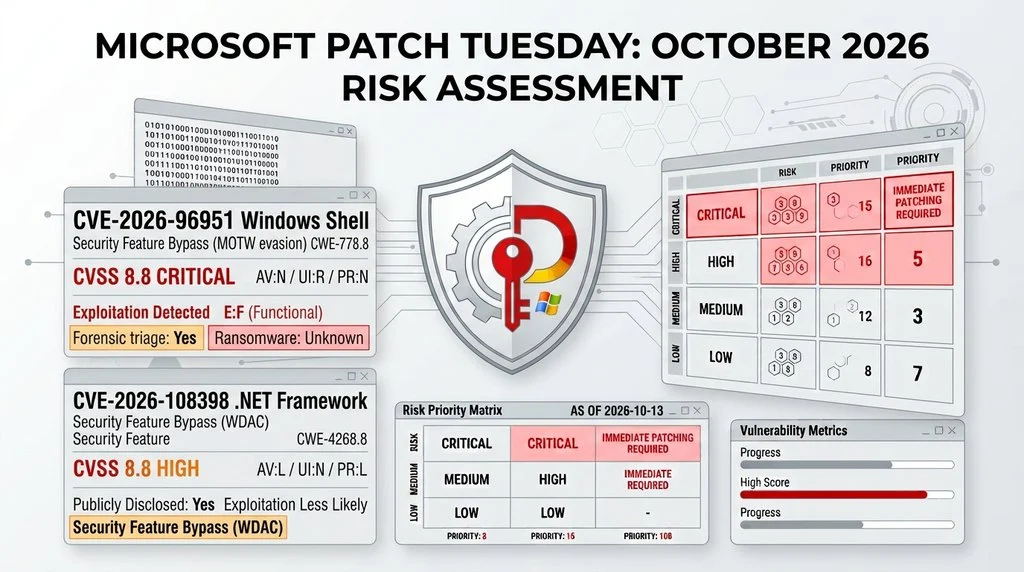
This release also feature 58 Microsoft CVEs with a 9.8 score, of which Microsoft rates 17 of them Critical, and none carry an “Exploitation More Likely” flag. What important is the exploited vulnerability and five Critical Outlook RCEs that are exploitable via the Reading Pane, and unauthenticated network RCEs that land on domain controllers. As always I rank on CISA BOD 26-04’s risk variables, not count or CVSS. One caveat as of now: NVD, the CVE Program records and other metadata was not populated at the time of publication. So, CISA-ADP SSVC and EPSS values are marked pending and my own inferences are labelled as mine. Once available, I will update this post and will give me a good data point to improve. CISA did list the zero-day on KEV today though!
Microsoft Patch Tuesday October 2026: Zero-day, Publicly Disclosed CVEs
| CVE | Component / type | CWE | CVSS 3.1 | MSRC exploitability | KEV / due / triage | Affected (CPE family) |
|---|---|---|---|---|---|---|
| CVE-2026-96951 | Windows Shell Security Feature Bypass (MOTW evasion) | CWE-77 | 8.8AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:H/E:F | Exploited: Yes Exploitation Detected | KEV: added 2026-10-13 Due: 2026-10-16 Forensic triage: Yes Ransomware: Unknown | cpe:2.3:o:microsoft:windows_10_1607 through windows_11_26H1, windows_server_2012_R2 through windows_server_2025, plus outlook.com |
| CVE-2026-108398 | .NET Framework Security Feature Bypass (WDAC) | CWE-426 | 8.8AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H/E:U | Publicly Disclosed: Yes Exploitation Less Likely | Not exploited per MSRC. KEV not expected. | cpe:2.3:a:microsoft:.net_framework, .net |
CVE-2026-96951: Windows Shell MOTW bypass
MSRC calls it command injection in Windows Shell that lets an unauthenticated attacker bypass a security feature over the network via the “Mark of the Web” feature. Delivery mechanism can be an email or an instant message with a crafted file, and the user has to act on it. The temporal vector says E:F, functional exploit code exists.
What is unknown: the file type or container used in the observed exploitation. Fortunately, the fix ships in the Windows cumulative updates.
CVE-2026-108398: .NET Framework WDAC bypass
Untrusted search path (CWE-426), when an authenticated local attacker places a crafted .NET assembly and registers it for loading by a protected process, which gets around Windows Defender Application Control and lets unauthorised code run. It’s a local vulnerability and needs a foothold, so it’s not a super critical, front-door busting bug. It is exactly what you’d use after a phish to get past an allow-listing control, and the details are public. If WDAC is a control you lean on, move this up.
Prioritizing using BOD 26-04
BOD 26-04 needs four inputs: asset exposure (mine), KEV status, automatable and technical impact (CISA’s, via KEV and CISA-ADP SSVC). For the zero-day CISA has already spoken: KEV-listed 13 October with a 16 October due date and forensic triage required. That is the 3-day tier, and it overrules my pre-release read, which had it in the slower internal tier because it needs a user to act. CISA-ADP SSVC values I couldn’t read; everything else below is my assessment, labelled.
CVE-2026-96951, Windows Shell MOTW bypass (exploited)
- KEV: YES, added 2026-10-13 (CISA)
- Forensic triage: YES (CISA)
- Automatable: NO (UI:R), my inference
- Exposure: user endpoint, my inference
CISA outcome: Tier 1, due 2026-10-16 + forensic triage
3-day due date. CISA treats it as the exposed tier despite UI:R.
Do: patch by Friday, and hunt for prior MOTW-less execution.
CVE-2026-70229, AD DS RCE 8.1 (Critical, Exploitation More Likely)
- KEV: NO (not exploited per MSRC)
- Impact: TOTAL (code exec on DC), my inference
- Automatable: NO (AC:H), my inference
Model outcome: Tier 4, about 60 days (DCs not exposed)
Unauthenticated network RCE on a DC; Microsoft rates it More Likely.
My override: tier-0 asset, patch domain controllers within 3 days.
BOD 26-04 parks anything not internet exposed in the slower tiers, by design. Five Microsoft Patch Tuesday October vulnerabilities sit on tier-0 systems where that breaks:
- CVE-2026-70229 (AD DS RCE, unauthenticated, More Likely),
- CVE-2026-96219 (LSASS RCE, 9.8, unauthenticated),
- CVE-2026-83869 and CVE-2026-96113 (two DNS Server RCEs at 9.8, and most AD-integrated DNS runs on DCs), and
- CVE-2026-69802 (NDES RCE, on your PKI).
I will prioritize patching the domain controllers and NDES/ADCS hosts on the 3-day clock whatever the model prints.
Additional Priority Microsoft Patch Tuesday October 2026 CVEs
Based on a simple criteria that uses: Microsoft “Critical”, “Exploitation More Likely”, a Reading or Preview Pane trigger, or an unauthenticated network 9.8, on services that sit on tier-0 or face the internet. Tiers are the BOD 26-04 model with my exposure and automation calls; none carry CISA values yet.
| CVE | Product | CVSS | CWE | MSRC | CPE family | Tier (my inference) |
|---|---|---|---|---|---|---|
| CVE-2026-70242, CVE-2026-70291, CVE-2026-88156, CVE-2026-97016, CVE-2026-97749 | Outlook RCE, triggered by viewing in the Reading Pane | 9.8 | CWE-122, CWE-121, CWE-415 | Critical, Less Likely | 365_apps, office_2021, office_2024 | Tier 2: mail is the exposure, no click needed |
| CVE-2026-96219 | LSASS RCE (crafted packet, no auth) | 9.8 | CWE-787 | Important, Less Likely | Windows client and server (21) | 3 days on DCs (override) |
| CVE-2026-83869, CVE-2026-96113 | DNS Server RCE x2 | 9.8 | CWE-191; CWE-122, CWE-197 | Important, Less Likely | Windows server and client (24; 10) | 3 days on DCs; Tier 2 if DNS is public |
| CVE-2026-70229 | Active Directory Domain Services RCE | 8.1 | CWE-863 | Critical, More Likely | Windows client and server (26) | 3 days on DCs (override) |
| CVE-2026-69802 | NDES RCE | 8.1 | CWE-1390 | Critical, Less Likely | windows_server_2012 to windows_server_2025 (6) | 3 days on PKI (override) |
| CVE-2026-70571 | Exchange Server RCE (crafted email, content conversion) | 8.1 | CWE-121 | Critical, More Likely | exchange_server_2016, _2019, _se | Tier 2: exposed + automatable + total |
| CVE-2026-70279 | Exchange Server spoofing (crafted link to an admin) | 9.3 | CWE-79 | Important, More Likely | exchange_server_2016, _2019, _se | Tier 2 if OWA is internet facing |
| CVE-2026-96940 | Exchange OWA EoP (cross-mailbox read) | 8.8 | CWE-1390 | Important, More Likely | exchange_server_2016, _2019, _se | Tier 2 if OWA is internet facing |
| CVE-2026-85792, CVE-2026-85809, CVE-2026-85806, CVE-2026-100222, CVE-2026-84015 | RRAS x2, NPS x2, PPP EAP-TLS RCE | 9.8 | CWE-416, CWE-122, CWE-121, CWE-191 | Important, Less Likely | Windows client and server | Tier 2 on VPN/RADIUS edge |
| CVE-2026-97816 | OpenSSH for Windows RCE | 9.8 | CWE-416 | Important, Less Likely | Win10 1809 to Server 2025 (21) | Tier 2 where sshd is reachable |
| CVE-2026-83910 | RPC Runtime RCE | 9.8 | CWE-787 | Important, Less Likely | Windows client and server (26) | Tier 3; every host |
| CVE-2026-100202, CVE-2026-108460 | MSMQ RCE x2 | 9.8; 8.1 | CWE-416 | Critical, Less Likely | Windows client and server | Tier 3; Tier 2 if TCP 1801 exposed |
| CVE-2026-100219, CVE-2026-105016 | Microsoft QUIC RCE x2 | 9.8 | CWE-416, CWE-122 | Critical, Less Likely | Windows 11, Server 2022/2025, .NET | Tier 3; Tier 2 if UDP 443 exposed |
| CVE-2026-96934 | DHCP Server RCE (failover) | 9.8 | CWE-416 | Critical, Less Likely | Server 2012 to 2025 | Tier 3 |
| CVE-2026-70147, CVE-2026-70153 | PostScript Printer Driver RCE | 9.8 | CWE-122 | Critical, Less Likely | Windows client and server | Tier 3 |
| CVE-2026-70187 | Remote Desktop Gateway RCE | 8.1 | CWE-416 | Critical, Less Likely | Server 2012 to 2025 | Tier 4 by model; I’d do 14 days, it faces the internet |
| CVE-2026-108463 | SmartScreen bypass (crafted install link) | 8.8 | CWE-41 | Important, Less Likely | Windows 11 24H2 to 26H2 (8) | Tier 4; pairs with the MOTW zero-day |
| CVE-2026-105733 | Hyper-V RCE (nested guest escape) | 8.8 | CWE-1419 | Critical, Less Likely | Win10 21H2 to Server 2025 | Tier 3 on multi-tenant hosts |
| CVE-2026-102866 | SharePoint SE EoP (proof token) | 8.1 | CWE-347 | Critical, Less Likely | sharepoint_server:subscription | Tier 4; Tier 3 if internet facing |
| CVE-2026-88159 | BITS RCE | 8.8 | CWE-125 | Important, More Likely | Windows client and server | Tier 4 |
| CVE-2026-102217 | WebDAV EoP (code as IIS app pool) | 8.8 | CWE-41 | Important, More Likely | Windows client and server | Tier 4; Tier 3 where WebDAV is on |
Fourteen of these Microsoft Office RCEs list the Reading or Preview Pane as an attack vector, of which five Outlook CVEs are scored at 9.8, 4 PowerPoint, three affect Word and two Excel. The five Outlook bugs are the worst of the lot because no file has to be opened and simply viewing the message is enough. Microsoft lists a total of 109 CVEs that are “Exploitation More Likely“, most of them local EoP. Among them are five Windows Update EoPs (CVE-2026-69673, CVE-2026-69718, CVE-2026-69733, CVE-2026-69783, CVE-2026-69882) with link-following and search-path CWEs, plus Servicing Stack (CVE-2026-96939), Error Reporting Service, Audio Service, Mobile Broadband and Health and Optimized Experiences.
58 CVEs score 9.8. None is exploited, none is More Likely.
Microsoft Patch Tuesday October 2026: Numbers
From Microsoft's release note: 1,413 Microsoft CVEs across 176 distinct updates. By family: Windows 1,102, Office 134, Developer Tools 61, SharePoint 36, Other 32, SQL Server 22, Azure 15, Exchange 7, Defender 4, Edge 0, plus the republished Talos CVE-2026-21413 (Raw Image Extension).
The October 2026 CVRF itself lists 1,759 entries: 1,413 Microsoft-CNA CVEs, one advisory (ADV260001, ReFS hardening on removable media) and 342 third-party CVEs Microsoft republishes for its own Linux distribution. Microsoft rates 76 Critical and 1,337 Important. It documents zero workarounds and zero mitigations, so patching is the only reduction on offer. This is the breakdown:
October 2026 by type (1,413 Microsoft CVEs)
How many are “Critical”? Depends who you ask
Microsoft Patch Tuesday October 2026: Unauthenticated attack surface and Microsoft's exploitability assessment
Classifying the 1,413 Microsoft CVEs into two parts:
- The first is the CVSS base vector: Privileges Required
PR:Nmeans the attacker needs no account, and addingAV:NandUI:Nmeans no account, over the network, without any user action. - The second is Microsoft's Exploitability Index for the latest software release. Most treat it as a forecast of whether working exploit code is likely.
Put together, they show where the unauthenticated surface is and how much of it Microsoft expects to see attacked.
Exploitability assessment by privileges required
| Privileges required | Detected | More Likely | Less Likely | Unlikely | N/A | None given | Total |
|---|---|---|---|---|---|---|---|
| None (PR:N) | 1 | 3 | 349 | 85 | 4 | 0 | 442 |
| Low (PR:L) | 0 | 106 | 692 | 147 | 3 | 1 | 949 |
| High (PR:H) | 0 | 0 | 18 | 6 | 0 | 0 | 24 |
| No CVSS vector | 0 | 0 | 1 | 0 | 0 | 0 | 1 |
| Total | 1 | 109 | 1060 | 238 | 7 | 1 | 1416 |
Of the complete list, 442 CVEs (31%) need no privileges. Only four of them have a "Detected" or "More Likely".
No-privilege CVEs by attack vector and user interaction
| Attack vector | No user interaction (UI:N) | User interaction (UI:R) | Total PR:N |
|---|---|---|---|
| Network (AV:N) | 173 | 223 | 396 |
| Adjacent (AV:A) | 10 | 1 | 11 |
| Local (AV:L) | 1 | 20 | 21 |
| Physical (AV:P) | 14 | 0 | 14 |
| Total | 198 | 244 | 442 |
173 CVEs are reachable over the network with no account and no click (AV:N/PR:N/UI:N). This is the set of CVEs to check against your exposure inventory. Additional 223 CVEs need a user to take an action.
Network, no auth, no click: by type and exploitability (173 CVEs)
| Type | More Likely | Less Likely | Unlikely | N/A | Total |
|---|---|---|---|---|---|
| Remote Code Execution | 2 | 67 | 14 | 2 | 85 |
| Elevation of Privilege | 0 | 7 | 0 | 0 | 7 |
| Information Disclosure | 0 | 14 | 2 | 2 | 18 |
| Denial of Service | 0 | 31 | 16 | 0 | 47 |
| Security Feature Bypass | 0 | 6 | 0 | 0 | 6 |
| Spoofing | 0 | 4 | 4 | 0 | 8 |
| Tampering | 0 | 2 | 0 | 0 | 2 |
| Total | 2 | 131 | 36 | 4 | 173 |
85 of the 173 are RCEs and 28 of those are rated Critical. 58 of the 173 score 9.8; none is flagged More Likely. Only two zero-click remote CVEs carry More Likely, and both are already in my priority list: AD DS (CVE-2026-70229) and Exchange (CVE-2026-70571). Both have AC:H, which is why CVSS scores them 8.1 rather than 9.8. The four N/A entries are cloud services (Azure App Service, API Center, HDInsight and Dataverse), where Microsoft doesn't give an exploitability forecast.
No-privilege CVEs that Microsoft rates Detected or More Likely
| CVE | Title | CVSS | Vector | Severity | Exploitability |
|---|---|---|---|---|---|
| CVE-2026-96951 | Windows Shell Security Feature Bypass Vulnerability | 8.8 | AV:N/AC:L/PR:N/UI:R/S:U | Important | Detected |
| CVE-2026-70279 | Microsoft Exchange Server Spoofing Vulnerability | 9.3 | AV:N/AC:L/PR:N/UI:R/S:C | Important | More Likely |
| CVE-2026-70229 | Windows Active Directory Domain Services Remote Code Execution Vulnerability | 8.1 | AV:N/AC:H/PR:N/UI:N/S:U | Critical | More Likely |
| CVE-2026-70571 | Microsoft Exchange Server Remote Code Execution Vulnerability | 8.1 | AV:N/AC:H/PR:N/UI:N/S:U | Critical | More Likely |
CVE-2026-70279 is the one this cut adds to my priority list. It's an Exchange spoofing bug (CWE-79, scope changed, 9.3): an unauthenticated attacker sends a crafted link, and if an Exchange admin clicks it, the attacker acts with that admin's privileges. More Likely, no auth, and it lands on an admin. I'd treat it with the other Exchange fixes, in days, wherever OWA is reachable.
Detection engineering
Coverage gaps first. The exploited bug is a trust-control bypass, so the pre-exploitation signal is an absence: a file that should carry Zone.Identifier and doesn't, or a prompt that never fired. Most network RCEs this month are memory-safety bugs (use after free and heap overflow lead the CWE table) with no published trigger, so the practical detection is a service crash followed by an odd child process. The .NET WDAC bypass is the reverse problem: the control you'd use to stop the payload is the thing being bypassed, so you need telemetry that doesn't depend on WDAC blocking.
| CVE | CWE | ATT&CK | Hunt (telemetry and behaviour) |
|---|---|---|---|
| CVE-2026-96951 | CWE-77 | T1553.005, T1566.001, T1204.002 | Sysmon 11/15: files written by Outlook, Teams or browsers to Downloads or the Outlook temp folder without a Zone.Identifier stream. Sysmon 1: explorer.exe spawning cmd, powershell, mshta, wscript or rundll32 within a minute of a user opening a mail attachment. Atomic Red Team's MOTW tests cover container formats; they won't tell you whether this specific bypass fires.Rules: Sysmon CVE-2026-96951-*; Sigma: script host from download path; SigmaHQ a018fdc3. The missing-MOTW check is a join (EID 11 with no EID 15 for the same file), so run it as a SIEM search. |
| CVE-2026-108398 | CWE-426 | T1574.001, T1685 | Sysmon 7 (image load): unsigned or newly written .NET assemblies loaded by protected processes. CodeIntegrity Operational events stop being useful if the bypass works, so baseline assembly load paths for protected processes and alert on new ones. Rules: Sysmon CVE-2026-108398-unsigned-userpath-load; Sigma: unsigned user-path DLL in system binary; HardBreacher unsigned System32 DLL load (same idea, System32 paths). |
| Outlook x5 (CVE-2026-70242 and peers) | CWE-122, CWE-121, CWE-415 | T1203, T1566.001 | Sysmon 1: OUTLOOK.EXE spawning anything other than Office and browser helpers. Application 1000 crashes of OUTLOOK.EXE clustered across users within minutes, which is how a mass-mailed trigger looks. Join to message trace for the common sender or subject.Rules: Sysmon Outlook-RCE-any-child; SigmaHQ 208748f7; Sigma: critical service crash. |
| CVE-2026-96219, CVE-2026-83869, CVE-2026-96113 | CWE-787, CWE-191, CWE-122 | T1210 | On DCs: lsass.exe or dns.exe crashes (Application 1000/1001), DNS Server service restarts (System 7031/7034), unexpected DC reboots. Any child process of dns.exe is an incident.Rules: Sysmon CriticalService-crash-WerFault, NetworkService-spawns-shell; Sigma: critical service crash; SigmaHQ a18e0862 (matches exception c0000001 only); SigmaHQ a4e3d776. |
| CVE-2026-70229 | CWE-863 | T1210 | Unexpected DC reboots (Event 1074/6008), and new services or scheduled tasks on DCs after a crash. |
| CVE-2026-70571 | CWE-121 | T1190, T1505.003 | Exchange transport and content-conversion processes crashing, then spawning shells. New .aspx files under the Exchange install path.Rules: Sysmon CVE-2026-70571-*; Sigma: script write to Exchange web dirs; SigmaHQ bd1212e5 (needs CommandLine on file events, so EDR data, not plain Sysmon). |
| CVE-2026-96940 | CWE-1390 | T1114.002 | Mailbox audit MailItemsAccessed where one authenticated user touches many other mailboxes via OWA. |
| CVE-2026-97816 | CWE-416 | T1190, T1021.004 | Inventory hosts with the OpenSSH Server feature enabled and TCP 22 reachable. sshd.exe crashes or child processes outside a normal shell session.Rules: Sysmon CVE-2026-97816-sshd-connection, CriticalService-crash-WerFault. |
| CVE-2026-100202, CVE-2026-108460 | CWE-416 | T1210 | Inbound TCP 1801 from outside the expected segment; mqsvc.exe crashes or child processes. Many hosts have MSMQ from old installers.Rules: Sysmon MSMQ-mqsvc-connection, NetworkService-spawns-shell; SigmaHQ 53207cc2. |
| CVE-2026-100219, CVE-2026-105016 | CWE-416, CWE-122 | T1190 | Inventory UDP 443 listeners (HTTP/3 in http.sys, SMB over QUIC). System or svchost crashes tied to msquic. |
| CVE-2026-96934 | CWE-416 | T1210 | DHCP failover traffic (TCP 647) from anything but the configured partner; DHCP Server crash and restart events. Rules: Sysmon DHCP-failover-647. |
| CVE-2026-105733 | CWE-1419 | T1611 | On Hyper-V hosts: any child process of vmwp.exe (the per-VM worker) other than WerFault, and vmwp.exe crashes.Rules: Sigma: vmwp.exe child process; Sysmon NetworkService-spawns-shell, CriticalService-crash-WerFault. |
| CVE-2026-70147, -70153 | CWE-122 | T1210 | spoolsv.exe or PrintIsolationHost.exe crashes and child processes on servers. Turn off print services on servers that don't print.Rules: Sysmon NetworkService-spawns-shell; SigmaHQ dcdbc940. |
| CVE-2026-69802 | CWE-1390 | T1649, T1190 | ADCS 4886/4887 issuance bursts from the NDES service account; IIS logs on the mscep endpoints from unexpected sources.Rules: Sigma correlation: 20+ issuances by one requester in 10 minutes. |
| CVE-2026-108463 | CWE-41 | T1553.005, T1204.002 | Installers launched from browser downloads where SmartScreen recorded no reputation check; pair with the MOTW hunt above. Rules: Sysmon CVE-2026-96951-browser-download-write. |
| Windows Update EoP x5 | CWE-59, CWE-426, CWE-73, CWE-77 | T1068, T1574 | Junction or symlink creation by standard users under C:\ProgramData and C:\Windows\SoftwareDistribution. Weak signal; Atomic Red Team has thin coverage for link-following EoP. |
Hunts this week
- Mail-delivered files reaching disk without
Zone.Identifier, joined to process creation fromexplorer.exe(CVE-2026-96951). OUTLOOK.EXEcrashes clustered across many users, and any shell spawned by Outlook.- New .NET assembly load paths in protected processes (CVE-2026-108398).
- Crash-then-child-process on DCs (
lsass.exe,dns.exe), Exchange, MSMQ, DHCP and the spooler. - Exposure inventory: TCP 1801, TCP 22 (OpenSSH on Windows), UDP 443 (QUIC), RD Gateway, OWA, RRAS and NPS (RADIUS 1812/1813), public DNS on Windows, NDES
mscependpoints.
My Microsoft Patch Tuesday October 2026 takeaways
- Patch endpoints for CVE-2026-96951 by Friday 16 October. CISA gave it a 3-day due date and requires forensic triage, so also hunt back through your telemetry for MOTW-less execution before the patch landed.
- Push the Office update to mail clients in the same wave. Five Critical Outlook RCEs at 9.8 that fire from the Reading Pane are also important.
- Patch domain controllers in the next few days and not weeks. AD DS is flagged "More Likely", and LSASS plus two DNS Server bugs add three more unauthenticated 9.8 paths to a DC.
- If WDAC is one of your controls, don't leave CVE-2026-108398 on normal cadence. It's public knowledge now, and is built for the step after a typical phishing attack.
- 58 CVEs at 9.8 and not one exploited or More Likely. CVSS puts 66 at 9.0 or above; my composite puts one at Critical. That gap is why I don't rank on CVSS.
Leave a Reply
You must be logged in to post a comment.