• Skip to main content
  • Skip to secondary menu
  • Skip to primary sidebar
  • About Me
  • Privacy Policy
  • Media Mentions

PenTestIT.com

Your source for Detection Engineering, Security Research and Adversary Simulation

  • Search Engine Dorks
  • RSS feed
You are here: Home / Archives for MITRE ATT&CK
Microsoft Patch Tuesday October 2026

Cyber Threat Intelligence

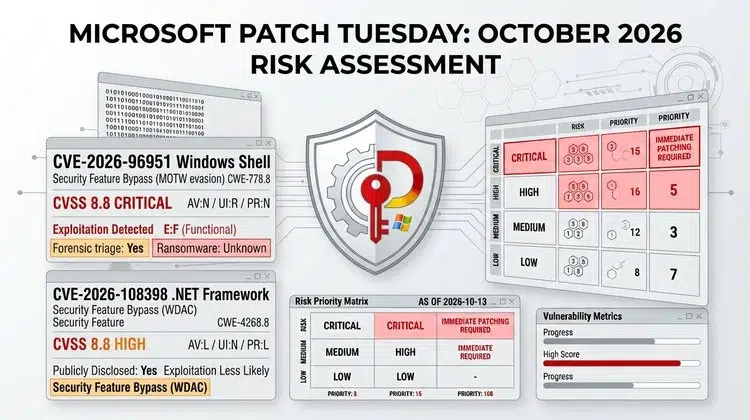
Microsoft Patch Tuesday October 2026 Exploitability and Patching Priority

This blog is my interpretation of the Microsoft Patch Tuesday October 2026 Exploitability and Patching Priority
Posted: Oct 14, 2026 by Mayuresh @pentestit Leave a Comment
Updated: Oct 16, 2026

Microsoft released this months bulletin a tad bit late. Nontheless, here it is! I half expected a crazy announcement - but fortunately other than crossing the total number of CVEs mitigated compared to the whole of 2025 - this release is nothing exceptional. This month, Microsoft patched 1,413 CVEs this month, plus one republished Cisco Talos CVE. Microsoft Windows alone Read more about Microsoft Patch Tuesday October 2026 Exploitability and Patching Priority
BigDiskBuster

Offensive Security

Analysing BigDiskBuster, the Microsoft Defender Update Blocker

This is my analysis of the BigDiskBuster - the open source Microsoft Defender Update Blocker.

Posted: Sep 27, 2026 by Mayuresh @pentestit
Updated: Oct 16, 2026

Last week Nightmare Eclipse open sourced BigDiskBuster - although I can see that now all the repositories have been made private. This post is my analysis of this tool that many news outlets called a "0day" initially. In reality, it is a class of defense-evasion tools that never touches a security product - Windows Defender in this case. It does not involve a driver unload, or Read more about Analysing BigDiskBuster, the Microsoft Defender Update Blocker

threat-report-killchain

Cyber Threat Intelligence

Claude Skill: threat-report-killchain

This post documents the features and working of a Claude skill that helps you automatically triage evidence backed threat intel reports.

Posted: Sep 19, 2026 by Mayuresh @pentestit
Updated: Oct 16, 2026

Everyday when I come across a threat intelligence report, I have to sift through a lot of data to get to the gist of it. Hence, I created this "threat-report-killchain" Claude skill to automate the process of CTI report triage for me. It does so completely, well 80% to be precise. Since, it helped me a lot, I thought of open sourcing it for the community. This post describes Read more about Claude Skill: threat-report-killchain

Essential Detection Engineering Metrics

Detection Engineering

Essential Detection Engineering Metrics

This is a list of essential detection engineering metrics.

Posted: Sep 1, 2026 by Mayuresh @pentestit
Updated: Oct 16, 2026

You have prioritized your threat detection backlog, but now want to quantify the progress. Throughout my career leading multiple threat detection engineering teams, I have relied on well-defined metrics to measure outcomes, demonstrate program value, and drive continuous improvement. In this post, I outline the detection engineering metrics I consider most important, spanning Read more about Essential Detection Engineering Metrics

List of Open Source C2 Post-Exploitation Frameworks

Offensive Security

List of Open Source C2 Post-Exploitation Frameworks

This is a list of open source C2 post-exploitation frameworks.

Posted: Feb 16, 2026 by Mayuresh @pentestit 1,472 views
Updated: Oct 16, 2026

Restoring this post with the help of the Wayback machine - This post has been lying in my drafts for more than a year with edits all over. But two days ago, it was announced that Powershell Empire would no longer be supported by it’s authors. Hence just like I curated a list of adversary emulation tools, I finalized this list of open source C2 post-exploitation Read more about List of Open Source C2 Post-Exploitation Frameworks

Adversary Emulation

List of Adversary Emulation Tools

This is a list of open source and commercial adversary emulation tools

Posted: Feb 12, 2026 by Mayuresh @pentestit 1,392 views
Updated: Oct 16, 2026

As I went through the logs on this blog, I saw that an old post from 2018 was still being requested for! Thanks to the internet gods, I was able to find a cached copy. Currently, this is a paste of the old adversary emulation post as is. But, I will update it in a few days time. Every once in a while, the security industry brings forth a new buzz word and introduces Read more about List of Adversary Emulation Tools

Primary Sidebar

Add PenTestIT as a preferred source on Google

Recently Updated

  1. The OpenAI Sophisticated Recording Device: Detection and Response – Part IUpdated Oct 17, 2026
  2. List of Open Source C2 Post-Exploitation FrameworksUpdated Oct 16, 2026
  3. Analysing BigDiskBuster, the Microsoft Defender Update BlockerUpdated Oct 16, 2026
  4. Analysis: CVE-2026-88771 and CVE-2026-88772Updated Oct 16, 2026
  5. List of Adversary Emulation ToolsUpdated Oct 16, 2026

Categories

  • Adversary Emulation
  • Cyber Threat Intelligence
  • Detection Engineering
  • Offensive Security
  • Open Source
  • Penetration Testing
  • Tools
  • Vulnerability Management
  • Vulnerability Research
  • Web Application Security

Archives

  • October 2026
  • September 2026
  • April 2026
  • March 2026
  • February 2026
  • August 2022
  • July 2020

Copyright © 2026 - PenTestIT.com | Information shared to be used for LEGAL purposes only!