Jump to section
This Microsoft Patch Tuesday March 2026 release addressed 93 vulnerabilities across Windows, Office, SQL Server, .NET, and Azure. Interestingly, two CVEs were publicly disclosed pre‑patch CVE‑2026‑21262 (SQL Server EoP) and CVE‑2026‑26127 (.NET DoS). However, unlike last month, no March CVE is confirmed exploited in the wild as of today. What is unusual is the fact that six of these Windows Elevation of Privilege vulnerabilities are listed as “Exploitation More Likely”.

Microsoft Patch Tuesday March 2026: Highlights
The following vulnerabilities were publicly disclosed, but not yet exploited:
- CVE-2026-21262 – SQL Server elevation of privilege could grant SQL sysadmin over the network. It is marked publicly disclosed and Microsoft’s Exploitability Index assessment is that “Exploitation Less Likely.”
- CVE-2026-26127 – .NET DoS is publicly disclosed, and Microsoft’s Exploitability Index assessment is “Unlikely.”
- CVE-2026-26110 and CVE-2026-26113 are my favourite – Office remote code execution chain exploitable via Preview Pane, while CVE-2026-26144 allows exfiltration of data via a weaponized Copilot payload.
- CVE-2026-24291 (Accessibility), CVE-2026-24294 (SMB Core), CVE-2026-24289 (kernel memory/race), CVE-2026-25187 (Winlogon) and additional two kernel/graphics elevation of privilege are of concern because of their aggregate attack surface coverage.
- CVE-2026-26118 (Azure MCP Server Tools) may leak a managed identity token when the service calls an attacker URL.
- Notable product clusters:
- Windows component heavy month (39 count), followed by Office/SharePoint (11), Azure (9), .NET (3), SQL Server (3), Edge (1).
- Routing and Remote Access Service (RRAS) RCE triplets: CVE-2026-25172, CVE-2026-25173, CVE-2026-26111.
- AFD (WinSock) EoP quartlet: CVE-2026-25176, CVE-2026-25178, CVE-2026-25179, CVE-2026-24293.
- Excel fivelet (?!): 5 issues across RCE/ID (CVE-2026-26107/CVE-2026-26108/CVE-2026-26109/CVE-2026-26112/CVE-2026-26144).
- The ‘ol favourite Print Spooler RCE: CVE-2026-23669 (UAF style RCE).
Microsoft Patch Tuesday March 2026: New Vulnerable Product Families
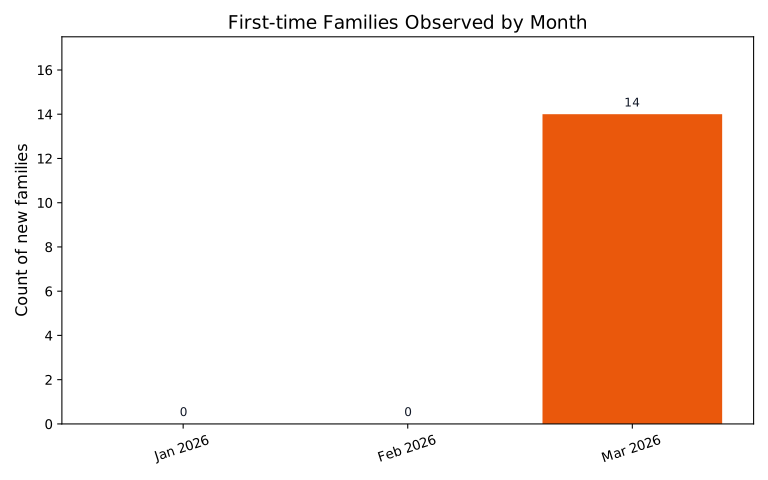
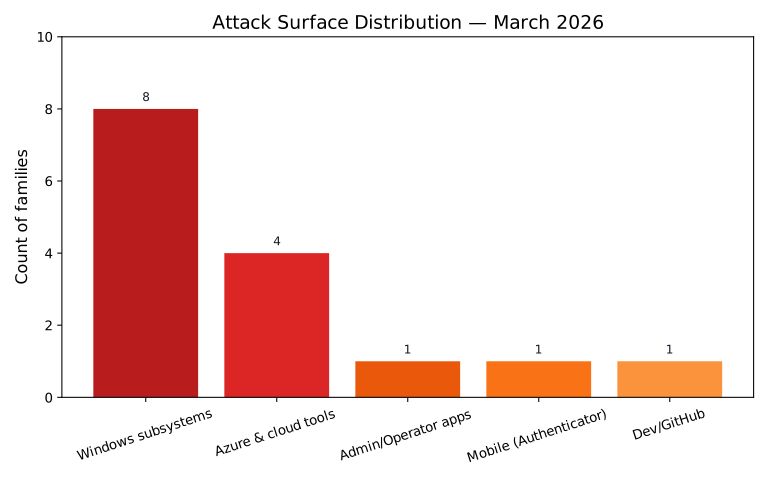
The Microsoft Patch Tuesday March 2026 release provides interesting insights by means of 14 new vulnerable product families. Compared to January and February, we got to see multiple Windows subsystems such as ProjFS, ReFS, UDFS, MapUrlToZone, Push Message Routing Service, Brokering FS, App Installer, System Image Manager and Azure/operator tools such as IoT Explorer, MCP, LAD, Arc Hybrid Worker vulnerabilities being fixed. Additionally, the Authenticator and a GitHub vulnerability were also mitigated. This vulnerability conjuncture stresses the high risk privileged workstations and cloud‑ops hosts present.
Microsoft Patch Tuesday March 2026: Product Attack Surface
This month, the product attack surface is quiet varied and has the following exploitable attack surface:
- 6 Windows elevation of privilege vulnerabilities are termed as “Exploitation More Likely.”
- 3 Critical vulnerabilities that require post-patch action such as the Office Preview Pane remote code execution vulnerabilities and the Excel information disclosure which are high risk even without active exploitation.
This is how I see the Microsoft Patch Tuesday March 2026 product attack surface:
Microsoft Patch Tuesday March 2026: Key Takeaways
These are my Microsoft Patch Tuesday March 2026 key takeaways:
- Highest ratio of “Exploitation More Likely” elevation of privilege vulnerabilities in 2026 so far. This is despite no confirmed exploited CVEs. This translates as this is a post intrusion hardening month. The risk is about what’s likely to come next, and not what’s active today. We should prioritize endpoint privilege escalation mitigation.
- Identity boundary risk via Azure MCP compromise (managed identity tokens). CVE-2026-26118 is not just an elevation of privilege. It’s abuse can leak a managed identity token across the cloud boundary. That can be worse than a local privilege escalation if tokens are reused.
- Privileged workstation concentration. Many affected components mitigated in the Microsoft Patch Tuesday March 2026 live only on admin/ops laptops and jump hosts (Arc Hybrid Worker, IoT Explorer, MCP, LAD, Authenticator). A compromise will magnify the blast radius if those endpoints lag patches.
- Excel disclosure meets Copilot. I treat CVE-2026-26144 as a multi surface exfiltration vector. Copilot amplification means leakage can extend beyond a single spreadsheet. Restricting macros and mark of the web (MoTW) controls should help in this regard.
- GitHub assigned CVEs are entering Patch Tuesday math. Some counts include a GitHub assigned CVE that signals that dependency CVEs will increasingly shape Patch Tuesday optics in the near future.
- RRAS & WinSock are a repeat from prior months. This indicates an ongoing effort in remediation in core networking surfaces.
- Print Spooler’s long history with vulnerabilities translates that any new Print Spooler RCEs as high risk even before PoCs land.