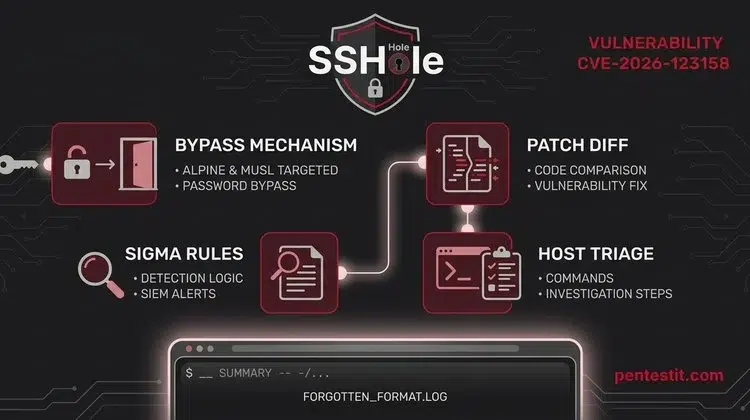
CVE-2026-123158 ("sshole") lets an unauthenticated attacker log into any OpenSSH account whose /etc/shadow password field is exactly * by sending a 257 to 1024 byte password. It only works when sshd is linked against musl libc, runs without PAM, has PasswordAuthentication yes, and at least one other local account holds a $5$ or $6$ hash. Fix: OpenSSH 10.6p2 or your distribution Read more about sshole (CVE-2026-123158): OpenSSH musl Password Bypass Root Cause, Detection and
sshole (CVE-2026-123158): OpenSSH musl Password Bypass Root Cause, Detection and Mitigation
On Alpine CVE-2026-12315 allows log into an account that has no password when three conditions are met!