• Skip to main content
  • Skip to secondary menu
  • Skip to primary sidebar
  • About Me
  • Privacy Policy
  • Media Mentions

PenTestIT.com

Your source for Detection Engineering, Security Research and Adversary Simulation

  • Search Engine Dorks
  • RSS feed
You are here: Home / Archives for Detection Engineering

Detection Engineering Archives:

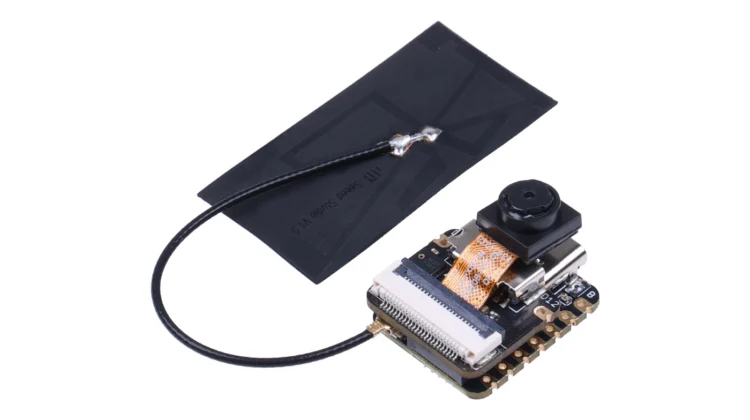
OpenAI Sophisticated Recording Device - XIAO ESP32-S3 Sense

Detection Engineering

The OpenAI Sophisticated Recording Device: Detection and Response

This is my post to help you in detection and response of the OpenAI recording device & similar devices when connected to an endpoint.
Posted: Oct 16, 2026 by Mayuresh @pentestit Leave a Comment

I came across the now viral OpenAI Newsroom post on X where an OpenAI engineer accused of planting a sophisticated recording device in an executive conference room. The device was a Seeed Studio XIAO ESP32-S3 Sense that was plugged into a USB port on the back of a TV. I missed the "back of a TV" part earlier and wrote this post with a endpoint - Microsoft Windows/Linux/Apple Read more about The OpenAI Sophisticated Recording Device: Detection and Response

Microsoft Patch Tuesday October 2026

Cyber Threat Intelligence

Microsoft Patch Tuesday October 2026 Exploitability and Patching Priority

This blog is my interpretation of the Microsoft Patch Tuesday October 2026 Exploitability and Patching Priority

Posted: Oct 14, 2026 by Mayuresh @pentestit Leave a Comment
Updated: Oct 16, 2026

Microsoft released this months bulletin a tad bit late. Nontheless, here it is! I half expected a crazy announcement - but fortunately other than crossing the total number of CVEs mitigated compared to the whole of 2025 - this release is nothing exceptional. This month, Microsoft patched 1,413 CVEs this month, plus one republished Cisco Talos CVE. Microsoft Windows alone Read more about Microsoft Patch Tuesday October 2026 Exploitability and Patching Priority

Introduction to jev

Cyber Threat Intelligence

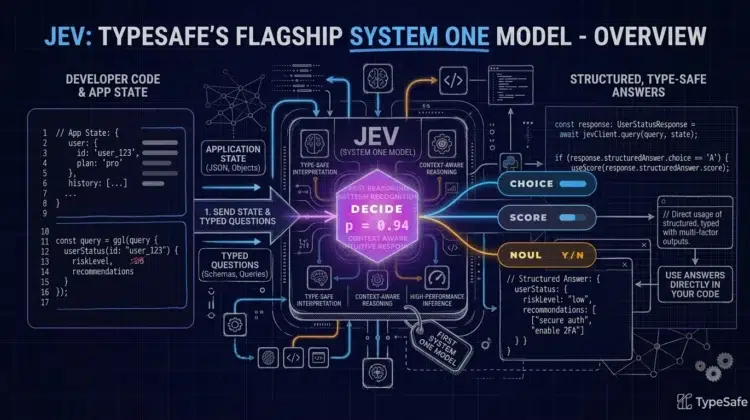
Introduction: Jev From A Security Practioner’s Perspective

This post introduces The TypeSafe AI Jev model and my perspectives as a security practitioner.

Posted: Oct 4, 2026 by Mayuresh @pentestit Leave a Comment

I know I'm a tad bit late with this post, but work took over and this post about the introduction to Jev stayed in drafts over two weeks. However, now, we are ready to go! TypeSafe AI released Jev on September 15, 2026. It's the first of what they call "System One" models. You don't chat with it, you just send it a state (text or JSON) and a set of typed questions, and it Read more about Introduction: Jev From A Security Practioner’s Perspective

Essential Detection Engineering Metrics

Detection Engineering

Essential Detection Engineering Metrics

This is a list of essential detection engineering metrics.

Posted: Sep 1, 2026 by Mayuresh @pentestit
Updated: Oct 16, 2026

You have prioritized your threat detection backlog, but now want to quantify the progress. Throughout my career leading multiple threat detection engineering teams, I have relied on well-defined metrics to measure outcomes, demonstrate program value, and drive continuous improvement. In this post, I outline the detection engineering metrics I consider most important, spanning Read more about Essential Detection Engineering Metrics

Detection Engineering

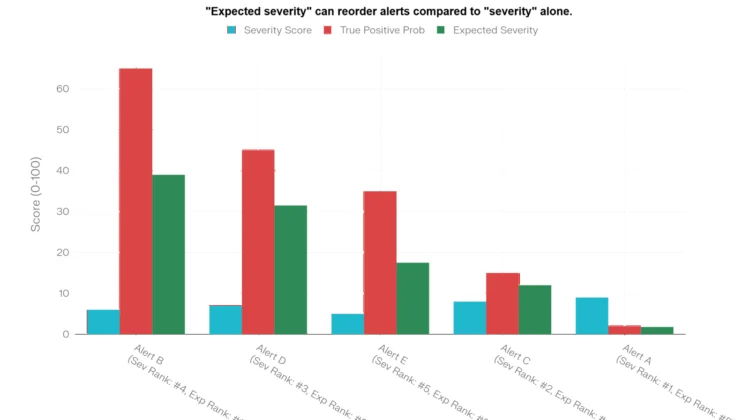
“Severity” or “Expected Severity” for Prioritization?

This post introduce the concept of "Expected Severity" for threat prioritization.

Posted: Apr 26, 2026 by Mayuresh @pentestit 756 views
Updated: Oct 16, 2026

In one of my last post - Prioritizing a Threat Detection Backlog, I talked about prioritizing your threat detection backlog. It is true when you run a program in an organization. However, when you consume security content from another organization, severity is often generalized. This is where, the concept of expected severity can help and I trust should be used more often. Let Read more about “Severity” or “Expected Severity” for Prioritization?

Detection Engineering

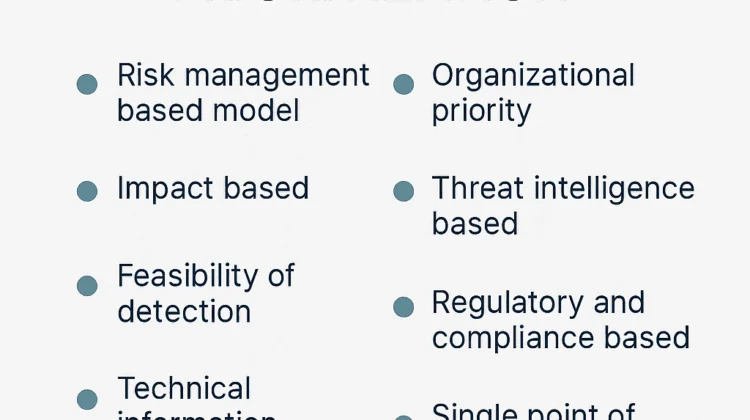
Prioritizing a Threat Detection Backlog

These are a few methods that you can use to prioritize a threat detection backlog

Posted: Feb 9, 2026 by Mayuresh @pentestit 1,127 views
Updated: Oct 16, 2026

Most security teams eventually hit the same problem - the list of “detections to build next” grows faster than the capacity to actually build, test, and maintain them. Inputs from red-team exercises, threat intelligence reports, new CVEs, leadership asks, compliance requirements, and plain hype can drive a perfect prioritization backlog haywire. Without a clear model for Read more about Prioritizing a Threat Detection Backlog

Primary Sidebar

Add PenTestIT as a preferred source on Google

Recently Updated

  1. List of Open Source C2 Post-Exploitation FrameworksUpdated Oct 16, 2026
  2. Analysing BigDiskBuster, the Microsoft Defender Update BlockerUpdated Oct 16, 2026
  3. Analysis: CVE-2026-88771 and CVE-2026-88772Updated Oct 16, 2026
  4. List of Adversary Emulation ToolsUpdated Oct 16, 2026
  5. “Severity” or “Expected Severity” for Prioritization?Updated Oct 16, 2026

Categories

  • Adversary Emulation
  • Cyber Threat Intelligence
  • Detection Engineering
  • Offensive Security
  • Open Source
  • Penetration Testing
  • Tools
  • Vulnerability Management
  • Vulnerability Research
  • Web Application Security

Archives

  • October 2026
  • September 2026
  • April 2026
  • March 2026
  • February 2026
  • August 2022
  • July 2020

Copyright © 2026 - PenTestIT.com | Information shared to be used for LEGAL purposes only!