php2shell is now a thing from the last week as PHP fixed CVE-2026-109618 and CVE-2026-109619 on 21 October. In the days leading upto the weekend, multiple proof-of-concept code were uploaded to GitHub and elsewhere. I’m publishing my algorithm to analyze repositories that are safe to run and which ones do their job. This analysis is based on the 1,414 repositories, uploaded and cloned between 23 and 25 October.
How do you score a GitHub PoC repository?
Now a days, everyone uploads all proof-of-concept codes to GitHub. However, how do you know whether the code in a repository is safe to run or whether it does what it claims. By 25 October, four days after PHP fixed CVE-2026-109618 and CVE-2026-109619, 1,414 repos claimed PoCs, scanners, patches and mitigations for them, and stars were the only ranking anyone had.
I remember starting with RepoMetaScore and the OpenSSF Scorecard to do this. However, either did not suit me. They are good measures of how well a maintained software project is run, which is a different question from what I wanted to do. I wanted to know if a PoC repo is safe to use and does what it claims among other things and php2shell was the perfect opportunity to test it out.
I started with a 19 indicator supply-chain rubric (account age, signed commits, PR review, pinned Actions) and dropped most of it. The measure project maturity that three-day-old repos never have as is the case in most 0day directories. 1,149 of 1,414 repos have a single author and only 311 have CI workflows. GitHub verifies signatures on 571 of them, and 496 of those carry only GitHub’s own key for commits made in the web interface, so a signature mostly proves someone used the browser. All four lure repos are fully signed that way. This is what the algorithm do:
- Verify safety for status every repo: Every repository gets a safety status first such as – do not use, no code, caution, or no red flags. Only defensive repos (scanners, patches, mitigations, detection rules and docs) then get a score out of 100.
- Reliability score: A PoC scanner accuracy that has lab results will override every rule. If PHP’s official fix, controls a mitigation actually applies, rules that load in Suricata, Sigma or YARA. If the code is original or copy, signatures GitHub verifies against the author’s own key, more than one author, owner account age, organization (verified domains score highest), there’s another score. If the repository does not contain any prebuilt executables in the repo or its releases, no curl into a shell, pinned dependencies, no default-branch history rewritten after publication, there’s an addition.
- Guardrails: Each score shows its coverage, such as “9 of 11”. Two scores above can add at most 20 points over the content share. The amount of stars and AI authorship aren’t scored as stars can be bought and AI PoC slop is often unreliable.
I ask Claude to create an infographic and this is the algorithm:
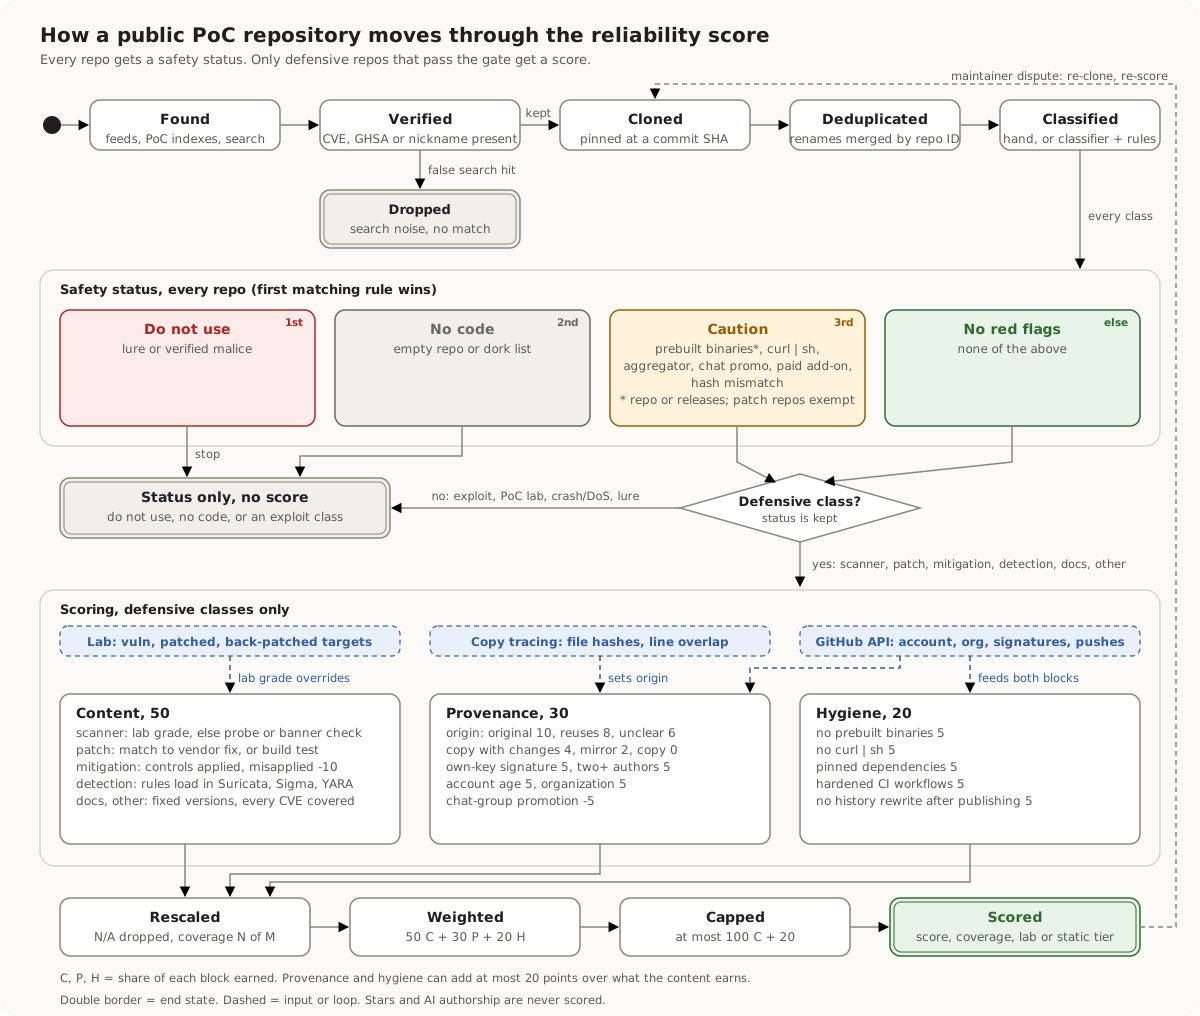
In short, this is the formula:
Score = 50 × content share + 30 × provenance share + 20 × hygiene share, capped at 100 × content share + 20. Each share counts only the indicators that apply to that repo, so a patch isn’t marked down for having no CI. The cap means a well-signed repo whose patch changes nothing still scores low.
Exploit and PoC repos get a safety status and no score. A ranked list of the best exploits is a shopping list, and I’m not publishing one.
Based on this algorithm, this is what the php2shell PoCs on GitHub look like. Most of these repos aren’t exploits at all. Scanners are the biggest group, and 989 repos (70%) have no stars.
What 1,414 PHP2Shell repositories actually contain
I validated some 470 repositories by hand and wrote an automatic classifier to complete the rest.
Which languages are the php2shell PoCs written in?
Python and shell scripts make up 62% of the set. PHP itself is the main language in only 106 repos, led by scanners (33) and PoC labs (25).
Primary language of 1,414 PHP2Shell repositories
CVE-2026-109618 and CVE-2026-109619: PoC Authors
Nearly a quarter of the repos say outright that an AI wrote some of the code. Repositories that removed the attribution don’t show up – unfortunately. Hence, I don’t score it: AI-written code can be right and hand-written code can be wrong.
Who wrote them, and what they claim
Safety status
Fortunately, I found no malware and no live callbacks. The two “do not use” repos are lures: one promotes a Telegram group and a paid scanner service, the other links a paid listing.
Safety status of 1,414 PHP2Shell repositories
What GitHub’s Repositories tell us:
- Young accounts: 62 of the 1,328 owners created their GitHub account in the 30 days before disclosure. They own 64 repos, spread across every class.
- Organizations: 129 owners are organizations; 18 have verified domains.
- Release downloads: 149 repos publish release files the clone doesn’t contain, and 73 that aren’t patch repos ship prebuilt executables or archives there. Each of those gets a caution. Patch repos that ship packages get a note to check checksums instead.
- Rewritten history: 124 repos force-pushed over their default branch after publishing. GitHub’s push events no longer say when a push was forced, so I found these by checking each push’s previous commit against my clones.
- Renames and empty repos: 8 renamed repos pointed at another repo already in the set and are counted once. 30 repos are empty: a name and nothing else.
- Stars: GitHub’s stargazer list is now limited to a repositories admins, so I used the 4,288 star events in the repos’ event feeds, from 3,516 accounts. The typical account was over six years old when it starred. One cluster stands out: 97 accounts created on 24 October each starred assetnote, 9bie or openai’s checker, a median of three minutes after signing up, and 74 of them are empty. That’s 7%, 3% and 1% of those repos’ stars. New users signing up to star a trending repo and a star service look the same in public data. Stars aren’t scored either way.
The lab-verified scores
40 scored repos went through a real test: 37 scanners against four PHP targets, and three community backports built into PHP 7.4.33. pentestershell’s scanner was tested too, but the repo also ships exploit code, so it has a status and no score. These are the scores I’d trust most.
assetnote/php2shell-scanner
- Content 44 of 50: correct on all four targets
- Provenance 30 of 30: verified org, verified signatures, older account
- Hygiene 15 of 20: unpinned dependencies
89
Sends probe requests and reads the response. Coverage 12 of 12.
Use
offseq/php2shell-poc
- Content 50 of 50: correct on all four targets
- Provenance 18 of 30: single author, unsigned
- Hygiene 20 of 20
88
Its OOM check reports a reachable trigger only on unpatched PHP. Coverage 11 of 11.
Use the OOM check
Anton-Barinov/php2shell-patches
- Content 50 of 50: matched the official fix and kept upload progress working
- Provenance 16 of 30: shares files both ways with another repo, unsigned
- Hygiene 16 of 20: unhardened CI workflow
82
Coverage 12 of 12. The 8.1 variant drops PHP's opcache and error-state changes; read from the patch, not tested.
Use the 7.4 enhanced patch
zarguell/php2shell-scanner
- Content 35 of 50: active check right on all four, version check flags the back-patched host
- Provenance 25 of 30: verified signatures, more than one author
- Hygiene 15 of 20: unpinned dependencies
75
Reports VULNERABLE(oracle) and LIKELY_VULNERABLE(version) separately; only the first held up. Coverage 13 of 13.
Trust its oracle verdict only
vegeta2206/php2scan
- Content 44 of 50: correct on all four targets
- Provenance 9 of 30: copy of assetnote with changes, single author
- Hygiene 20 of 20
73
85% of its code lines match assetnote's scanner. Coverage 11 of 11.
Use assetnote's original
mspiq/php2shell-scanner
- Content 20 of 50: flagged the back-patched target as vulnerable
- Provenance 15 of 30: single author, unsigned, no org
- Hygiene 15 of 20: unpinned dependencies
50
Was 80. It reads the version from phpinfo, and my earlier back-patched target leaked the real 8.4.27 there. Coverage 13 of 13.
Confirm by advisory
appsec-cz/php-eol-patch
- Content 28 of 50: fixes the session path, handles OOM the same as unpatched
- Provenance 16 of 30: single author, unverified org, includes files from another repo
- Hygiene 20 of 20
64
Coverage 10 of 10.
Prefer the official patch
Bhavye-Malhotra/php2shell-2026
- Content 0: same as unpatched PHP on every test
- Provenance 17 of 30
- Hygiene 20 of 20
20
Capped: provenance and hygiene can't lift a patch that changes nothing. Coverage 10 of 10.
Do not rely on it
Everything else
The other 990 defensive repos are scored from static checks plus GitHub’s API data. Treat this as a shortlist to read, not a verdict.
| Class | Repos | Median | 80 or more | Under 50 | Highest static scores |
|---|---|---|---|---|---|
| Scanner / triage | 443 | 60 | 0 | 63 | SGit-AI (78), Trupal25 (77) |
| Patch / backport | 188 | 63 | 31 | 34 | bogdik (90), fiecar (90) |
| Mitigation | 116 | 71 | 27 | 10 | syhunt (93), pichuang (92) |
| Detection rules | 59 | 52 | 5 | 27 | rjmendez (90), umbrasec-labs (85) |
| Docs | 75 | 78 | 35 | 17 | Akirapl (95), NCSC-NL (91) |
| Other | 109 | 68 | 35 | 29 | allixsenos (92), WaldemarEnns (90) |
Static scores rest on code, text and account data, not tests. The best static scanners, SGit-AI at 78 and Trupal25 at 77, haven’t been tested. Of the 37 scanners I did test, 5 got every target right. A high mitigation score means the repo applies its controls well, not that it protects you; no config change closes both bugs.
How the scores spread
How 1,030 reliability scores spread
Most repos land between 50 and 79. Only 15 score 90 or more. The 186 under 50 are spread across classes: 68 scanners, 35 patches, 29 other, 27 detection repos, 17 docs and 10 mitigations. Stars and the score barely agree: the rank correlation is 0.10 across the 1,030 graded repos.
Why do php2shell scanners flag patched servers?
Ubuntu, RHEL and cPanel ship fixes without changing the version number. I served four targets (vulnerable 8.4.26, patched 8.4.27, patched with the version hidden, and fixed code that reports 8.4.26 in every header and page) and ran 46 scanners against each, in their default modes.
46 php2shell scanners against four lab targets
Only five told the back-patched host apart from the vulnerable one, and two of those five are built on assetnote’s code (85% and 77% of their lines). mspiq, which I’d graded correct on 23 October, reads the version from phpinfo. My first back-patched target leaked the real 8.4.27 there. A real back-patched build doesn’t, so I fixed the target and mspiq now gets the same false positive as the rest.
Reading the version from X-Powered-By or phpinfo gets distro fixes wrong every time. Confirm distro fixes by vendor advisory or package changelog, and pick a scanner that sends a probe and reads the response.
Do the public php2shell PoCs actually work?
Finally,
CVE-2026-109619: session upload progress
- 8.4.26: the upload-progress handler resolves classes and runs the unserializer before the request starts
- 8.4.27: clean result, no user code runs
- Both rfc1867 session tests fail on 8.4.26 and pass on 8.4.27
Real on default settings
The primitive the gadget PoCs need is present on unpatched defaults.
Code execution still needs a usable gadget in the target app and an ASLR defeat, which is why the serious repos only demo against their own lab.
Patch first
CVE-2026-109618: out-of-memory state corruption
- 8.4.26: a huge per-part header count exhausts memory mid-parse
- 8.4.27: all 11 OOM and rfc1867 tests pass
- Getting from the crash to code execution depends on build, extensions and allocator
Trigger is reliable
Most 109618 repos show a crash or DoS, not RCE.
Patch, watch hosts
Interestingly, Hunt.io saw php2shell scanning switch to the user-agent php2shell-109618 at 20:36 UTC on 21 October. I searched my clones and GitHub’s code search for it and for Hunt’s two other indicator strings, php2shell-scan/109618 and php2shell-verify/1.0.
| Repo | Created (UTC) | Sends | Note |
|---|---|---|---|
| zhaoboy9692/CVE-2026-109618 | 21 Oct 03:24 | php2shell-109618 | earliest; copied verbatim by charindithjaindu |
| cereZ23/php-up-2026 | 21 Oct 07:40 | php2shell-109618 | shares a framework with zhaoboy9692 |
| darkfibr/php2shell-detect | 21 Oct 08:31 | php2shell-109618 | a scanner |
| eness PoC (983★) | 21 Oct 08:31 | php2shell-109618 | in its 109618 PoC from 08:46 until removed on 22 Oct |
| CYB3RW07F, giagara, Ghxstsec, JohnHansonTheDev, k3nundrum, Faizan-Khanx, ethernet8023 | 21 Oct 09:50 to 18:37 | php2shell-109618 | several inherit it from eness |
Twelve repositories sent php2shell-109618 before the scanner adopted it. The two earliest sources are zhaoboy9692 and eness, and copies of both carried it on, that fits a botnet reusing public PoC code. A user-agent is a string anyone can copy, so it’s a lead and not a proof. Five later repos send the same strings too, including test harnesses that mimic the scanner, and 40 more only quote them in detection rules.
Want to have a detailed look at the data collected? Here it is: The 1,030 defensive repos, highest score first within each class. Coverage counts the indicators that applied to that repo. “Lab” means the score rests on a real test. Safety “clear” means no red flags found, not proven safe. Exploit and PoC repos, lures and empty repos have a safety status only; they are in the CSV with everything else.
As of now, all of us must be content with exploits to the vulnerability like the StealMyBitcoin-PoC and Cloudflare CTF. These primarily seem to rely on the fact that the CTF environments run with php -S under default settings resulting in display_errors=On being enabled within the environment. So far we haven’t found a solution to the ASLR bypass that doesn’t involve triggering an OOM in php_session_send_cookie or rely on display_errors=On for exploitation purposes.